The problem
Generating a two-factor code from a raw secret usually means pasting that secret into a site you have to trust, or installing an app.
What I did
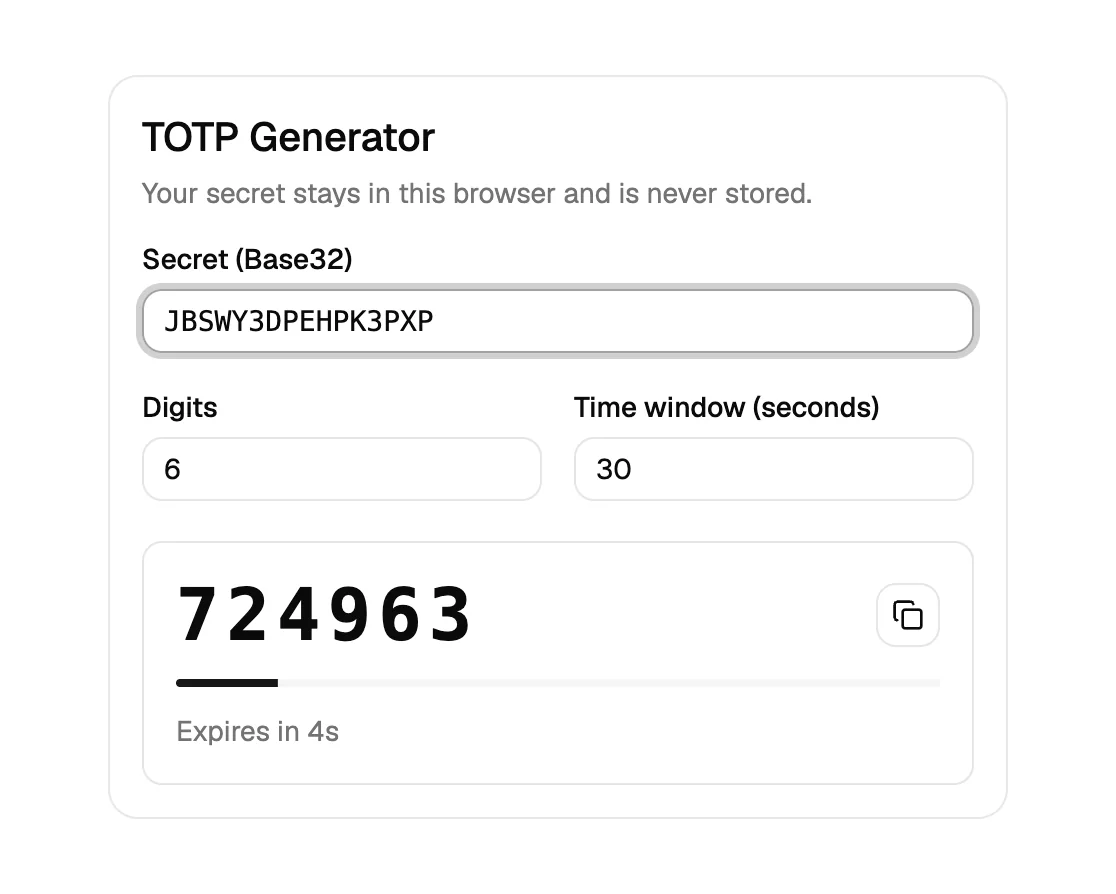
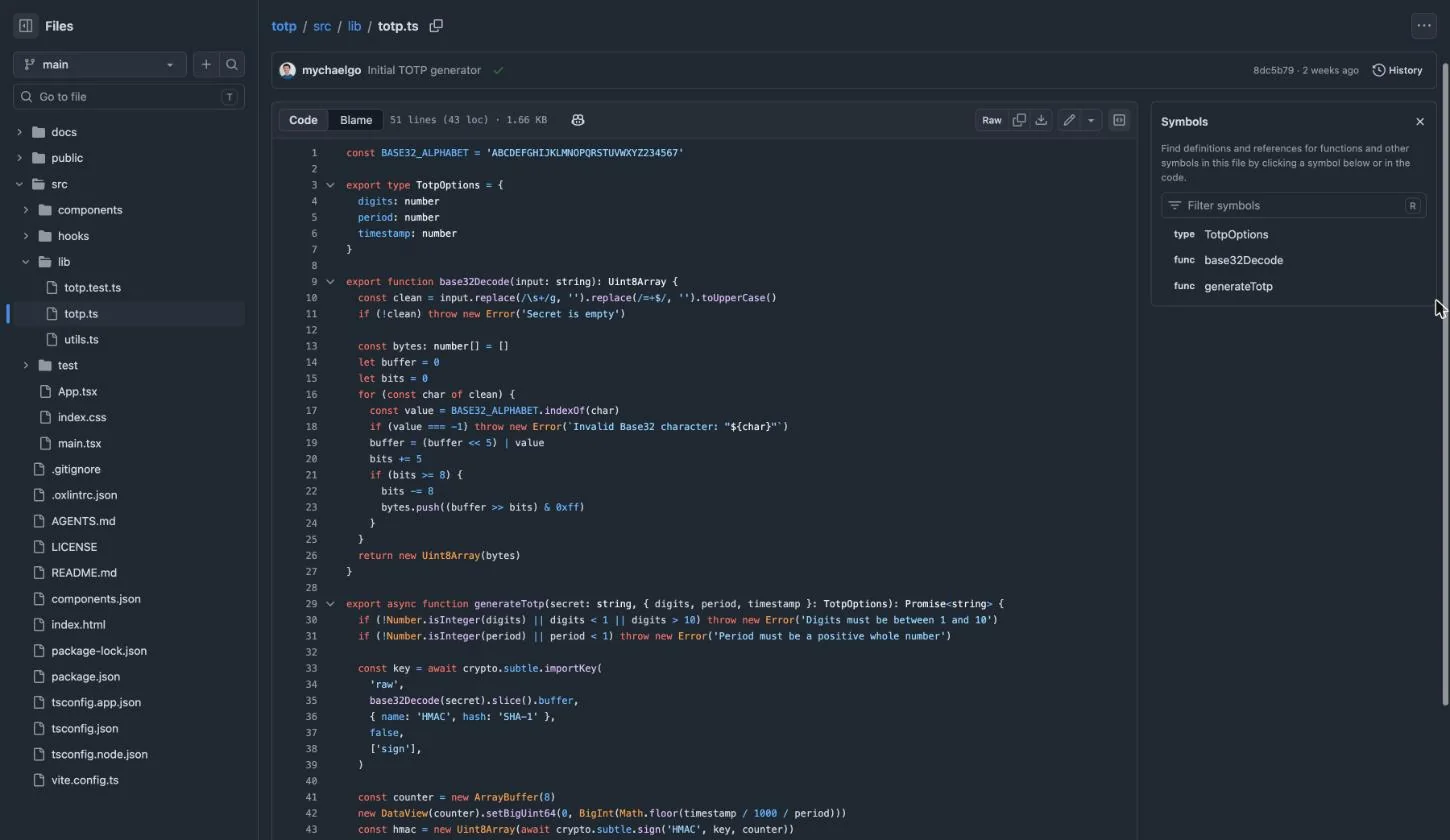
- Implemented TOTP (RFC 6238) with the Web Crypto API: Base32 decoding, HMAC-SHA1 and dynamic truncation, so the secret never leaves the browser and is never stored.
- Built a mobile-friendly UI in React with Tailwind CSS and shadcn/ui: configurable digits and time window, a countdown bar and one-tap copy.
- Tested the algorithm against the official RFC 6238 test vectors with Vitest and React Testing Library.
Screenshots
Reading this with an AI tool? Get this page as Markdown.